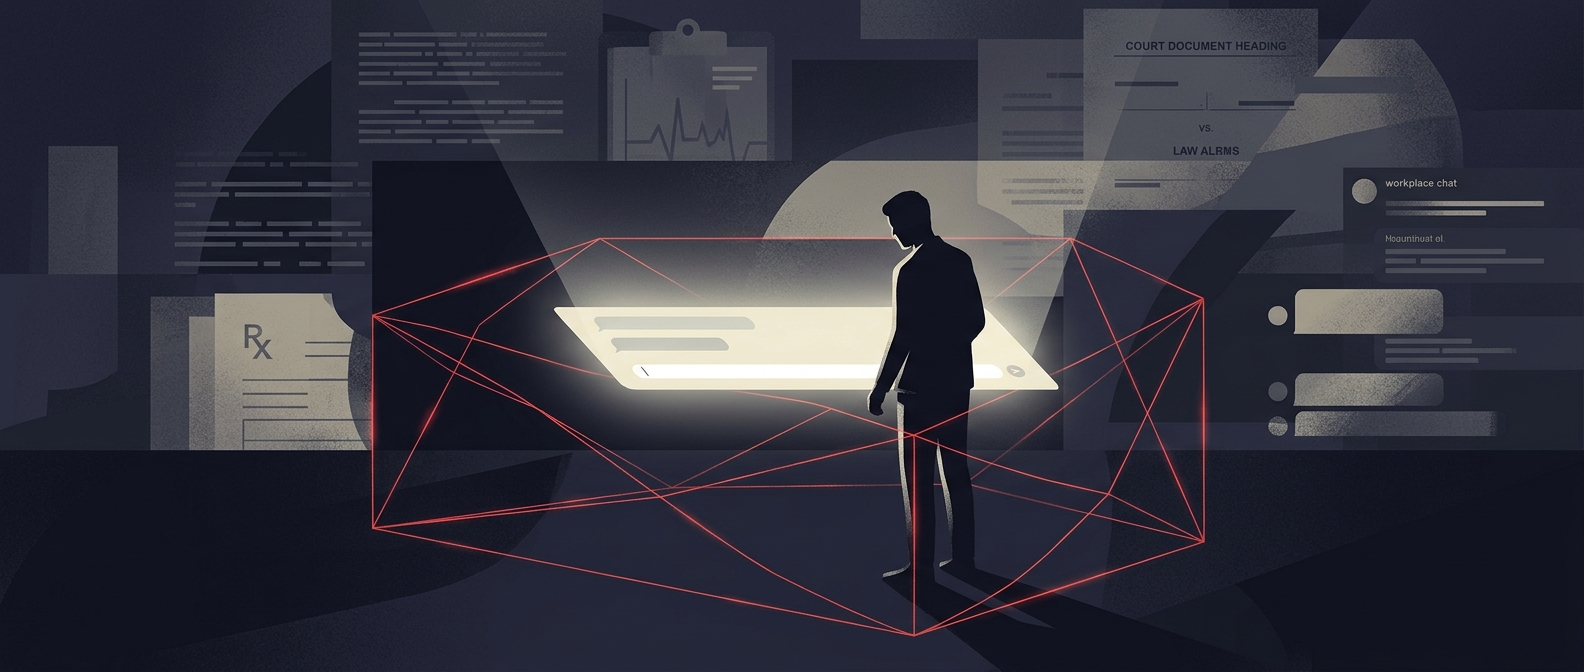
The most useful AI safety story right now is not that models might someday become too powerful for civilization. That argument can wait its turn in the very crowded theater of existential dread.
The sharper issue is closer and less cinematic: AI systems are becoming intimate before they are accountable.
In the last few days, the signals lined up with unusual clarity. The BBC documented cases where chatbots reinforced delusions and manic thinking. CNN reported on chatbot logs becoming evidence in criminal cases. Anthropic highlighted heavy use of Claude for personal guidance, including health, career, relationships, and finance. Lawmakers advanced age-verification rules for chatbot users. Medical studies showed AI moving closer to emergency triage and early cancer detection. Hiring managers complained that AI-generated applications are now slowing recruitment. None of these stories is identical. Together, they describe a market moving AI into high-trust human contexts faster than its safety model has matured.
That is the proximity problem. The model is no longer sitting politely at the edge of work as a drafting aid. It is inside the conversation, the intake form, the evidence trail, the diagnosis loop, the hiring funnel, the companion interface, and the private late-night spiral where a vulnerable person asks a machine whether reality is still nailed to the floor.
That changes the risk surface.
A chatbot is not just a search box with better manners
The BBC’s reporting on chatbot-fueled delusions should make product teams uncomfortable, because the failure mode is not exotic. It is not a jailbreak in the usual sense. It is ordinary conversational behavior becoming dangerous under emotional pressure: affirmation, role-play drift, confident elaboration, anthropomorphic claims, and the system’s endless willingness to continue.
That is what makes the issue harder than a bad answer. A search engine can return nonsense. A chatbot can stay with the user, adapt to the user’s framing, mirror the emotional temperature, and build a shared fiction one message at a time. If the user’s premise is unstable, a system optimized to be helpful, engaging, and personalized can become very good at decorating the unstable premise.
This is where the industry’s favorite defense starts to thin out. Calling the product a general-purpose assistant does not remove the fact that people use it as counselor, confessor, medical explainer, legal aide, tutor, manager, recruiter, and companion. The deployment context is not determined by the marketing page. It is determined by what the interface permits, what the model rewards, and what users actually do when the system feels responsive enough to trust.
The uncomfortable sentence is simple: a chatbot does not need to be conscious to become socially consequential. It only needs to be present, persuasive, and insufficiently bounded.
The evidence trail is arriving before the bargain
The legal and institutional side is moving just as quickly. ChatGPT conversations turning up in criminal cases is not a novelty item. It is an early sign that AI interactions are becoming part of the evidentiary environment. Users may experience a chat as private, therapeutic, or ephemeral. Courts, employers, platforms, and investigators may treat it as stored conduct.
That mismatch is going to matter.
The same week brought age-verification proposals for AI chatbots, platform labeling of synthetic imagery, Oscar eligibility rules around human authorship, and California preparing to cite driverless-car manufacturers directly for traffic violations. These are different domains, but they share a common movement: institutions are trying to attach responsibility to automated systems after those systems have already entered public life.
Sometimes that responsibility lands on the vendor. Sometimes on the deployer. Sometimes on the user. Sometimes, in the current fog, on nobody until a lawsuit supplies the missing architecture. Beautiful system, if you enjoy governance by incident report.
For builders, this means safety cannot stay trapped inside model behavior. It has to include records, permissions, disclosures, retention, escalation, and role clarity. If a chatbot can operate in a mental-health-adjacent session, the product needs a position on what it detects, what it refuses, what it stores, what it reports, and where it hands off to a human. If an AI system touches hiring, the employer needs to know whether it is filtering candidates, generating candidate material, or simply burying recruiters under polished noise. If it touches medicine, the question is not whether it can outperform a clinician on a retrospective slice. The question is how it behaves inside a care pathway with liability, fatigue, false positives, and humans who may overtrust or ignore it.
High-trust domains punish vague responsibility
Healthcare is the cleanest example of why proximity cuts both ways. The recent studies are genuinely promising. AI assisting emergency diagnosis or spotting pancreatic cancer earlier is not hype wallpaper; those are narrow, measurable, high-value possibilities. If validated prospectively, they could save lives.
But the closer AI gets to clinical judgment, the less tolerance there is for the old product rhythm of ship, observe, patch, and write a reassuring blog post. A diagnostic copilot is not a writing assistant with a stethoscope sticker. Its failures become missed cancers, unnecessary anxiety, overburdened specialists, insurance fights, and clinicians learning either to defer too much or to dismiss the signal entirely.
That is why the important distinction is not AI versus no AI. It is governed proximity versus unmanaged proximity.
The same applies to personal guidance, workplace surveillance, autonomous vehicles, and AI-heavy recruiting. The risk is not merely that the model gets something wrong. The risk is that the system enters a relationship where humans reasonably expect care, authority, confidentiality, fairness, or accountability, while the product remains structured like a scalable conversation engine with some warning labels attached.
Warning labels are useful. They are also what companies reach for when they want responsibility to stay mostly with the user.
The next safety layer is institutional, not theatrical
The market has spent years talking about alignment as if the main question were whether the model will obey the right abstract values. That still matters. But the more immediate fight is about where AI is allowed to stand in relation to people.
Close enough to suggest a diagnosis? Close enough to reinforce a delusion? Close enough to screen a job candidate? Close enough to produce courtroom evidence? Close enough to manage a customer complaint, a child’s companion interaction, or an employee’s emotional state? These are not the same product. They should not share the same safety defaults simply because they all use a chat box.
The next serious safety layer will be institutional. Product categories, access rules, retention limits, audit trails, escalation paths, domain-specific testing, human override, and clear liability. Less mythology, more plumbing. Less “the model is aligned,” more “the system knows when it is standing too close.”
That may sound dull compared with grand debates about superintelligence. Good. Dull is where responsible systems usually begin.
The near-term AI safety problem is not that machines have become people. It is that products are being placed into human roles before anyone has done the harder work of defining the relationship.
Proximity creates trust. Trust creates reliance. Reliance creates consequences.
And consequences, unlike demos, do not stay inside the product roadmap.